Security assessment
DVWA Vulnerability Assessment
Hands-on security testing of the Damn Vulnerable Web Application in a lab environment.
01 — Target & scope
Target & scope
- Target
- DVWA (Damn Vulnerable Web Application) in a local lab
- Scope
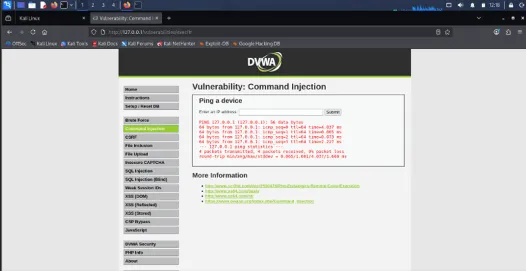
- Authentication validation, file upload validation and input field validation.
02 — Methodology
Methodology
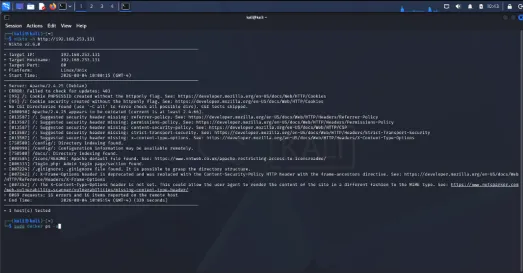
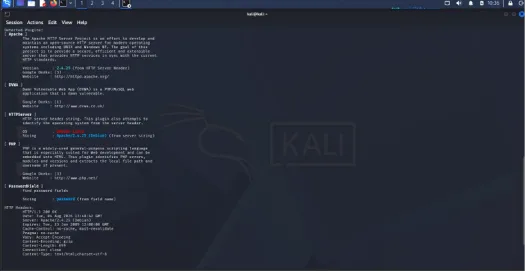
Tested each of the three areas against the lab application and recorded the results.
03 — Evidence
Evidence